

Jason Lee
Co-Head, Legal & Regulatory
Temasek
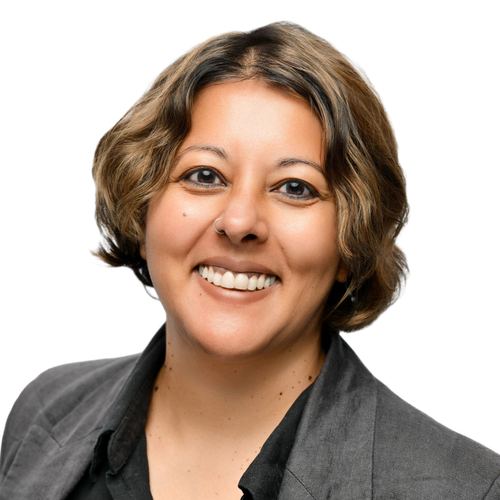
Jason Lee is currently Joint Head, Legal & Regulatory in Temasek where he leads the Regulatory & Compliance function. He has more than 20 years of experience providing legal and regulatory advice in global financial markets. Jason’s areas of expertise are in complex derivatives, financial regulation (including sanctions and financial crime), technology and data, commodities, and FDI regimes. He has also led and managed restructurings and workouts, regulatory investigations and compliance programs across diverse business areas and geographies. Jason is an active participant in various industry bodies and initiatives and speaks regularly at industry events. Jason is qualified in four different jurisdictions has practiced in a variety of in-house and practice roles in London, Singapore, and Sydney.
Speaking At
-
9:45–11:15amMon 16 NovPublic-Private RoundtableRoundtable Room 2Open
Accountability & Liability In Agentic Systems
Build, Buy, or Own: Strategies for Responsible AI Adoption in Finance
-
 Bojan ObradovicGroup Head of Innovation & Digital PartnershipsHSBC
-
 Jason LeeCo-Head, Legal & RegulatoryTemasek
-
 Jeremy HorExecutive Director, Enterprise Knowledge DepartmentMonetary Authority of Singapore
-
 Louise JohnstonDigital Assets & Blockchain, Global PolicyMastercard
-
 Norbert IzerExecutive Director for Financial Markets & DigitalizationCentral Bank of Hungary (Magyar Nemzeti Bank, MNB)
-
 Sunayna TutejaFormer Chief Innovation OfficerFederal Reserve System
-
 Varun KapoorDirector, Digital Strategy Group (FSI)Adobe
-
 Dr. Zhao JingyuanHead, Group Data OfficeOCBC
-
 Nilanshuk HaldarVice President – Global Head of Partnerships & AlliancesNucleus Software
-
 Prof. Heng WangProfessorSingapore Management UniversityModerator
-
 Kaitlyn ThinnChief Strategy OfficerGlobal Finance & Technology Network (GFTN)Moderator
About this session
Financial institutions are moving well beyond experimentation with AI, deploying it across credit decisioning, fraud detection, and everyday employee workflows at genuine scale. But how they get there differs sharply: some are building their own foundation models on proprietary data to avoid depending on external providers with their most sensitive information; others adopt commercial AI tools but wrap them in anonymization and strict governance before sensitive data reaches them; and some capital allocators are treating AI infrastructure itself — compute, data centres, foundation models — as a strategic asset worth direct ownership.
Regulation is catching up fast and unevenly, with major regimes now treating data location and third-party AI access as a risk to be supervised, not just a technology choice. Given the different AI strategies already in motion, what would it actually take to make them interoperable, auditable, and defensible across jurisdictions?
-